Anthropic Moved Twice. OpenAI Moved Twice. The Trust Boundary Moved With Them.
A tale of two cities. SaaS wants your data. The regulated enterprise wants it back. In the same fortnight the vendors chose sides, Grafana, Mistral, OpenAI, and GitHub were breached by the same threat actor.
Anthropic moved twice in fifteen days. OpenAI moved twice in seven days. That is the signal of the year.
The two companies that defined cloud-native AI in 2022 each made two distinct customer-side decisions in the same fortnight, independently, without coordinating, and with the same mechanism: engineers embedded inside the customer’s perimeter. When the two model labs that define a category each move the same direction twice in fifteen days, the move is the category.
The fortnight that produced those four decisions also produced two more from Palantir and Dell, and three confirmed breaches that cut through the developer-tool supply chain those vendors all run on. The opening day of the sequence was May 4, when Palantir reported 85% revenue growth in Q1 with AIP positioned as an operational system that runs inside the customer’s ontology, and on the same day Anthropic announced a $1.5 billion enterprise AI services joint venture with Blackstone, Hellman & Friedman, and a global investment bank, backed additionally by Apollo Global Management, General Atlantic, Leonard Green, Singapore’s GIC, and Sequoia, to embed Anthropic engineers directly inside the portfolio companies of the world’s largest PE firms. Seven days later, OpenAI launched DeployCo, a $4 billion business unit that embeds engineers inside client organizations, on the same day the supply chain attack reached two OpenAI employee devices. Seven days after that, OpenAI announced its second customer-side move: Codex, with more than 4 million weekly developers, deployed into hybrid and on-premises enterprise environments via the Dell AI Data Platform, on the same morning Dell announced AI Factory with NVIDIA at $50 billion FY27 projection. The next day, Anthropic shipped self-hosted sandboxes and MCP tunnels for Claude Managed Agents, its second customer-side move in fifteen days. And that evening, GitHub confirmed the third major breach in the campaign.
Count them: six vendor moves toward the customer perimeter, three confirmed breaches, one threat actor. They are not coincidental. They are the visible portion of a structural reorganization of where the trust boundary in enterprise AI sits. The conventional shorthand for this reorganization is the on-prem movement. That shorthand is wrong. What is happening is more specific, more permanent, and more architecturally consequential than “on-prem.”
This is a tale of two cities. The vendors live in one. The regulated enterprise lives in the other. For three years they pretended to live in the same place. The May 2026 announcements and the TeamPCP campaign ended the pretense in the same fortnight.
City One: the SaaS vendor
The SaaS-native AI vendor builds a coherent and defensible model. The data lives in the vendor’s environment. The runtime lives in the vendor’s environment. Usage signals feed back into the vendor’s product. The flywheel produces better models, faster iteration, and lower per-query costs than any single customer could achieve alone. The customer gets capability they could not build. The vendor gets scale they could not buy. The arithmetic is sound.
The vendor’s view of the trust boundary is also coherent. The vendor invests in certifications, residency options, encryption at rest and in transit, audit logs, and a public security posture. The customer accepts the vendor’s perimeter as their own by inheriting it. This is how every cloud-native enterprise tool was sold from roughly 2014 to 2024. It worked because the data being processed was, in the main, not the kind of data that produces a regulator’s attention when it leaves the building.
For AI, the arithmetic still works for most workloads. Marketing copy, internal search, code completion, customer service routing, document summarization. These are workloads where the vendor’s perimeter is an acceptable trust boundary, and where the flywheel produces value the customer rationally chooses not to forgo.
It is the next tier of workloads where the arithmetic breaks. And it is breaking visibly in the May 2026 numbers. The two companies that defined the cloud-native AI model in 2022 each made two distinct customer-side decisions in the same fifteen-day window. The mechanism is the same in all four: engineers embedded inside the customer’s perimeter.
City Two: the regulated enterprise
The regulated enterprise has been operating with a different definition of the trust boundary for forty years. The bank’s authority over what happens to a customer transaction does not stop at the bank’s firewall. It runs to the regulator, the auditor, the audit committee, the board, and the criminal liability that attaches to the executive officer at the top of the org chart. The same is true for a hospital under HIPAA, an asset manager under the SEC, a life sciences company under the FDA, a payments business under PCI, and a critical infrastructure operator under the regional cybersecurity authority.
The trust boundary for these institutions has never been the data center wall. It has been the institution’s accountability for the action taken on its authority, evidenced to a regulator who will examine the institution and not the institution’s vendor.
For most cloud workloads, this distinction did not matter operationally. The data was bounded. The actions were bounded. The vendor’s controls were close enough to the institution’s accountability that the gap could be closed by contract.
AI agents broke the bounding. An agent is not a workload. It is an actor. It takes actions on the institution’s authority, including actions the institution did not anticipate, in tool combinations the institution did not design, against systems the institution must answer for. The action is the regulated object. The regulator does not care whose cloud the action emanated from. The regulator cares whose authority the action was taken under, and what evidence the institution can produce that the action was authorized at the moment it executed.
That definition of the trust boundary is not satisfied by a vendor SOC 2 report. It is not satisfied by data residency. It is not satisfied by encryption at rest. It is satisfied by the institution’s own runtime control plane, the institution’s own evidence pipeline, and the institution’s own identity authority extending to every non-human actor in the system.
In other words, the trust boundary for AI has to live inside the institution’s accountability. Where the bytes physically sit is downstream of that.
The forcing functions
The shift to City Two is not preference. It is forced. Five regulatory and operational forcing functions have converged in the last twelve months.
The first is the Digital Operational Resilience Act. Since January 17, 2025, every regulated financial institution operating in the EU has been required to maintain ICT risk management programs, third-party AI risk assessments, incident reporting on tiered windows, and continuous evidence of control effectiveness. In my reading, a vendor’s unilateral change to its AI data policy is a third-party ICT risk the institution has to assess and document, not a settings change.
The second is SR 26-2, the Federal Reserve and OCC and FDIC joint guidance issued April 17, 2026. SR 26-2 retired SR 11-7 and explicitly carved generative AI and agentic AI out of the model risk management framework, leaving their governance to each bank’s own risk-management and governance practices. U.S. banks above $30 billion in assets must therefore construct their own AI governance architecture without relying on vendor-side framework inheritance. The carveout is a budget signal. The architecture has to be the institution’s, not the vendor’s.
The third is the May 2026 TeamPCP supply chain campaign. Over a single nine-day window, the same threat actor used three different vectors to breach four vendors in the developer-tool supply chain that AI agents now inhabit. On May 11, a malicious npm package compromised 170 packages across the TanStack ecosystem, Mistral AI’s SDK, UiPath, OpenSearch, and Guardrails AI. It was the first documented case of a malicious npm package carrying valid SLSA provenance, the cryptographic certificate that is supposed to prove a package was built from a trusted source. The trust marker itself was forged. Two OpenAI employee devices were compromised by the same attack, on the same day OpenAI launched DeployCo to put its engineers inside customer organizations. On May 16, the same campaign reached Grafana Labs through a stolen GitHub token from a misconfigured CI workflow; Grafana’s codebase was exfiltrated and the company refused the ransom. And on May 19, the same threat actor reached GitHub’s internal source through a poisoned VS Code extension on an employee device, exfiltrating 3,800 internal repositories.
Three vectors. One threat actor. Four vendors breached in nine days. The supply chain that hosts AI coding agents, MCP servers, and every productivity extension is the supply chain that just had its cryptographic integrity guarantee defeated, its CI pipelines exfiltrated, and the largest source code platform in the world reached at the internal perimeter.
The fourth forcing function is the agent sprawl problem. Vision Compliance reported in April that 78% of enterprises are unprepared for the EU AI Act and 83% have no AI inventory. OutSystems reported that 97% of enterprises run AI agents and only 12% have centralized control. Deloitte’s 2026 State of AI in the Enterprise report confirmed the same direction: only one in five organizations has a mature model for governing autonomous AI agents. IBM’s Institute for Business Value put systemic AI governance maturity at 21%. Three different research firms, same finding, same direction.
The fifth is the CEO-awareness layer. By mid-May 2026 the Forbes Business Council was running pieces by CEOs telling their peers that AI governance must be CEO-owned, citing the same Deloitte and IBM findings, and naming the August 2026 EU AI Act deadline (since deferred to 2 December 2027 for high-risk systems) as the forcing function. The conversation has reached the executives whose budgets will fund the architectural answer.
The combination of these five forcing functions is the gravitational mass that is pulling the vendors customer-side. The numbers in Palantir’s Q1, the $1.5 billion Anthropic-Wall Street joint venture, the $4 billion OpenAI DeployCo, Dell’s $50 billion FY27 AI server projection, the OpenAI Codex on-prem partnership at Dell Technologies World, and Anthropic’s self-hosted sandbox roadmap are the visible response. The TeamPCP campaign over the same nine days is what makes the response strategic instead of optional.
On-prem is the wrong word
The temptation, looking at the six vendor moves in the last 22 days, is to call this an on-prem revival. It is not.
Of the six moves, only Dell’s AI Factory is on-prem in the 2010 sense. The Anthropic-Wall Street consultancy JV puts engineers inside customer organizations but the inference runs in Anthropic’s environment. Anthropic’s self-hosted sandbox can run on AWS or Cloudflare or Vercel. OpenAI DeployCo embeds engineers inside the institution but the inference still runs in OpenAI’s environment. OpenAI Codex with Dell runs inside the customer’s data center but over OpenAI’s model behind the scenes. Palantir’s AIP can be deployed in dedicated cloud, customer cloud, or government cloud, with the operational control surface inside the institution’s authority regardless.
What is consistent across the six moves is not the topology. It is the trust boundary. The control surface around AI, the identity, the policy decisions, the evidence collection, and the runtime authorization is moving inside the institution’s accountability. The bytes can sit in many places. The accountability cannot move.
This is why the right word is the trust boundary, not on-prem. What matters is that the identity, the policy decision points, the evidence pipeline, and the runtime authorization live inside the institution’s accountability, wherever the workload runs.
The third pillar across topologies
This connects to a thesis I wrote in detail on May 15. Monitoring is crowded. Assurance is crowded. The third pillar of governed AI is AI Agent Operations, the continuous practice of operating an agent estate inside regulated environments. It is the layer that monitoring and assurance were not designed for, and the one regulators are converging on.
The third pillar discipline is topology-aware. Continuous monitoring works the same way wherever the workload runs. Continuous assurance works the same way. AI Agent Operations does not. It has to work the same way to the institution’s policy and evidence pipeline, but it has to bind to whatever runtime the institution has chosen. That is the architectural problem most current tooling does not solve.
Vendors of the next two years will be assessed on this. Can the same identity layer, the same policy decision point, the same evidence pipeline, the same runtime enforcement operate across every deployment the institution requires, with the same operating model and the same evidence grade. The institutions that buy AI infrastructure in 2026 are asking this question. Most vendors are not yet answering it convincingly. The TeamPCP campaign is the loudest reason to start.
What we are building
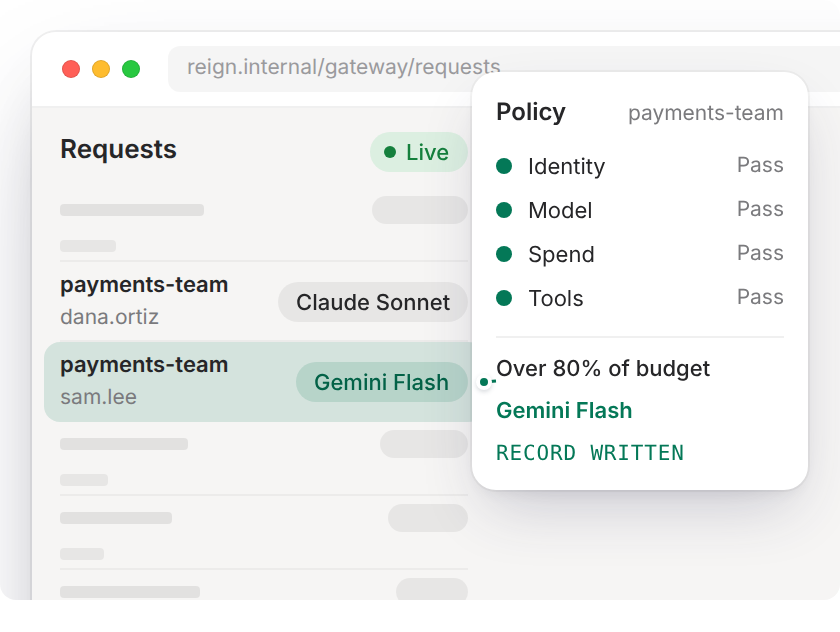
At iTmethods this is the architecture we have been building toward for the last 24 months. For AI calls sent through it, Reign Gateway applies identity, access, policy and spend controls, and creates a record of the request, the policy decision and the outcome. Reign Ops operates the engineering platforms inside the institution’s own trust boundary. Reign runs in a dedicated instance iTmethods operates or in the customer’s own AWS or Azure account. Air-gapped and sovereign deployment are supported.
The reason this matters is the reason this article exists. The institutions that are building governance for the agentic era are not betting on topology. They are betting on topology portability. The vendors that make portability operational, with evidence a regulator will accept, are the ones the regulated cohort will buy.
The bottom line
Six vendor moves, three breaches, one threat actor, twenty-two days. None of this is an on-prem revival. It is the early visible signal of a structural reorganization of where the trust boundary in enterprise AI sits.
TeamPCP did not invent the lesson. TeamPCP demonstrated it at every altitude of the supply chain in nine days. Grafana, Mistral, OpenAI, and GitHub all proved the same architectural point. The trust boundary cannot live inside the vendor’s perimeter. Every vendor’s perimeter can be breached. Including the largest ones in the world. Including the cloud-native AI vendors whose business model presumed otherwise.
Every enterprise AI conversation in 2026 is a topology conversation. Every topology conversation is a trust boundary conversation. Every trust boundary conversation is an accountability conversation. And accountability has only ever lived in one city.
The vendors are choosing sides. Two of them chose twice. The institutions chose sides forty years ago. The architecture is converging on what the institutions have always required.
On-prem is the wrong word. The trust boundary is the right one. And it has already moved.
Book a briefing
iTmethods runs the substrate inside the customer’s trust boundary. Reign Ops operates the engineering platforms inside the customer’s trust boundary. Reign runs in a dedicated instance iTmethods operates or in the customer’s own AWS or Azure account. Air-gapped and sovereign deployment are supported.
Book a briefingRelated reading
- Inside OpenAI, the Platform Team Is the New Trust Boundary (May 28, 2026)
- AI Agent Operations Is the Third Pillar of Governed AI (May 15, 2026)
- SR 26-2 Just Created a Governance Gap Banks Can't Ignore (May 12, 2026)
- Agent Sprawl Is the New Shadow IT. And the Numbers Are Worse Than You Think (May 5, 2026)
- The Deadline Moved. The Evidence Problem Didn't. (April 14, 2026)
Sources
- Palantir Q1 2026 earnings, May 4, 2026
- Anthropic + Blackstone, Hellman & Friedman and a global investment bank, Wall Street AI consultancy JV, May 4, 2026 (Fortune, CNBC, PYMNTS, SiliconANGLE)
- OpenAI DeployCo announcement, May 11, 2026
- TanStack npm supply chain attack disclosed, May 11, 2026 (TanStack postmortem; The Register; SafeDep; also Wiz, Snyk, Orca Security)
- OpenAI confirms two employee devices compromised, May 15, 2026 (The Register, The Hacker News)
- Grafana Labs breach confirmed, May 16, 2026 (BleepingComputer; SecurityWeek; also TechCrunch)
- Dell Technologies AI Factory with NVIDIA, May 18, 2026 (Dell Technologies World, Las Vegas)
- OpenAI + Dell Codex on-prem partnership, May 18, 2026
- Anthropic Claude Managed Agents self-hosted sandboxes and MCP tunnels, May 19, 2026
- GitHub internal repository breach confirmation, May 19, 2026
- Mistral AI source code listed for sale on Breached forum (CSO Online)
- TeamPCP attribution and SLSA provenance forgery (StepSecurity, Wiz)
- DORA Article 19 + ESA RTS on third-party ICT risk
- Federal Reserve SR 26-2, April 17, 2026
- Vision Compliance 2026 EU AI Act Readiness Report
- OutSystems 2026 Agentic AI Sprawl Research
- Deloitte 2026 State of AI in the Enterprise
- IBM Institute for Business Value AI Governance Maturity Report
- Forbes Business Council “Why Every CEO Needs an AI Governance Strategy Now,” May 18, 2026
Paul Goldman
Founder and CEO, iTmethods
Founder and CEO of iTmethods. Writes Securing the Agentic Era, essays on governing agentic AI in regulated industries. His team runs the platform, does the work, and proves it.