SR 26-2 Just Created a Governance Gap Banks Can't Ignore
The Federal Reserve just carved generative and agentic AI out of model risk management. The obligation to govern it did not go away. It moved to each bank.
On April 17, 2026, the Federal Reserve, OCC, and FDIC jointly retired SR 11-7, the 15-year-old framework that defined model risk management for every major U.S. bank, and replaced it with SR 26-2.
The financial press framed this as a modernization. More flexible, principles-based, less prescriptive. That framing misses the real story.
SR 26-2 does something much more consequential than update old rules. It explicitly carves generative AI and agentic AI out of scope and leaves their governance to each bank’s own risk-management and governance practices. The institutions reading this as regulatory relief are reading it backwards. The carveout is the spend signal.
What SR 26-2 Actually Does
The new guidance applies primarily to banking organizations above $30 billion in assets: every G-SIB and large regional bank. Two changes matter most.
1. Scope is drawn around risk-based model definitions, and generative and agentic AI sit outside it. A footnote leaves the governance and controls for anything outside the guidance to the bank’s own risk-management and governance practices. The principles in the guidance apply to traditional statistical and quantitative models and to non-generative, non-agentic AI models.
2. Materiality-based oversight replaces annual revalidation. Validation cadence is now driven by risk assessment rather than a fixed calendar.
The Real Impact. A Governance Gap That Didn’t Exist on April 16
For a Chief Risk Officer at a G-SIB, the shift is stark. Before SR 26-2 was issued on April 17, generative AI deployments were governed under an informal extension of SR 11-7. Now those same deployments sit outside any specific regulatory framework. The bank must now construct its own AI governance architecture under the risk-management and governance practices the guidance points it back to.
This is not theoretical. Banks above $30 billion in assets will be examined against SR 26-2’s expectations for the models it covers, and their generative and agentic AI work sits with the risk-management and governance practices each bank sets for itself. Those without a defensible AI governance framework mapped to AIGF v2.0, EU AI Act, OSFI E-23, and DORA will face a difficult conversation with their audit committee and board.
This is the operational consequence of the same architectural gap the Agent Sprawl piece documented on May 5. 97% of enterprises run AI agents. Only 12% have centralized control. SR 26-2 turns that 88-point gap into a question examiners will ask under each bank’s own practices, for U.S. banks above the $30 billion threshold.
The Spend Signal
SR 26-2 is the document that turns AI governance for generative and agentic AI from a discretionary line to an unavoidable one.
The institutions that started building enterprise AI governance frameworks ahead of SR 26-2, mapped to AIGF v2.0 and the EU AI Act, can already show their risk function and their examiners how these systems are governed. Banks that waited will be answering that question defensively, then facing what we estimate is an 18-month implementation cycle from a blank sheet.
The architectural pattern is the same one the Open RegTech piece of April 21 laid out: open standards (CDM, Morphir, DRR, AIGF v2.0) plus managed infrastructure to run them under SLA. SR 26-2 confirms why that pattern is the answer. The same evidence pipeline has to give a bank what each of SR 26-2, AIGF v2.0, third-party AI risk, OSFI E-23, the EU AI Act, and DORA asks for. One build. Six regimes.
SR 26-2 carved AI out. The obligation stays with you. The build is now.
The institutions that treat the carveout as relief instead of a budget signal will be, by our estimate, 12 to 18 months behind the institutions building evidence architecture today.
Book a briefingWhat Banks Should Build Now
Five capabilities, built on shared infrastructure, give a bank the evidence each of these regimes asks for: SR 26-2, AIGF v2.0, third-party AI risk, OSFI E-23, EU AI Act high-risk, and DORA. That is six regimes, one evidence pipeline.
- A continuously updated inventory of every model and AI system, scored on materiality.
- Identity and authorization for every non-human actor: models, agents, tools.
- Authoritative policy decisions in the operational path of every model and tool invocation.
- Evidence collection as a byproduct of operation, tamper-resistant, identity-attributed, mapped to regulatory clauses.
- Cross-domain consistency so the same evidence pipeline works for model risk, AI governance, trade reporting, and any regulated workflow.
These five together produce the evidence that SR 26-2 leaves each bank to produce, and that AIGF v2.0, the EU AI Act high-risk obligations, OSFI E-23, and DORA each ask for. They are not separate projects. They are one infrastructure problem.
The Bottom Line
The Federal Reserve, OCC, and FDIC just rewrote fifteen years of bank model risk management and left generative and agentic AI to the risk-management and governance practices each bank sets for itself. The institutions that treat the carveout as relief rather than a budget signal are reading it backwards.
The framework just got rewritten. Whatever controls a bank decides it needs, the architecture that evidences them is the same. The institutions that built for it already are the ones positioned for what comes next.
The carveout is where the next wave of regulated AI governance spend lands. The obligation moved to the bank the day the guidance issued.
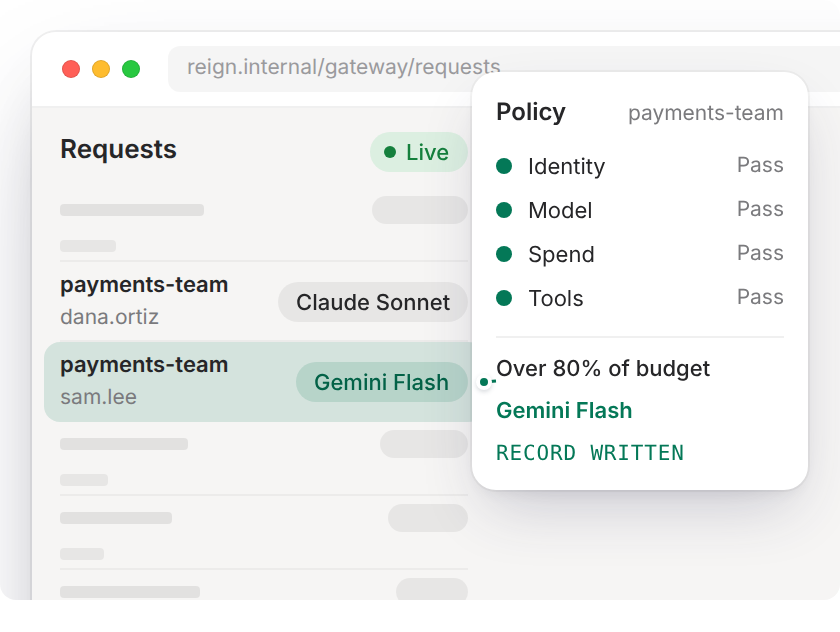
Reign Gateway records the AI traffic sent through it, in storage you own: one part of the evidence SR 26-2 leaves each bank to produce.
Sources
- Federal Reserve. SR 26-2 Letter (April 17, 2026)
- OCC. Bulletin 2026-13
- OCC. News Release 2026-29
- OSFI. Guideline E-23 Final, effective May 1, 2027
- FINOS AI Governance Framework v2.0. Addressing Agentic AI Risks
Paul Goldman
Founder and CEO, iTmethods
Founder and CEO of iTmethods. Writes Securing the Agentic Era, essays on governing agentic AI in regulated industries. His team runs the platform, does the work, and proves it.