Self-Hosted AI Agents Are Here. The Governance Isn't.
Cursor's self-hosted cloud agents are a proof point for the AI-native infrastructure shift. And a warning about the governance gap that enterprises must close.
On March 25, 2026, Cursor made self-hosted cloud agents generally available. This isn’t a minor feature update. It’s a structural signal about where enterprise AI development is heading, and what’s missing.
Cursor’s self-hosted agents are autonomous coding workers. Each gets its own isolated virtual machine with a terminal, browser, and full desktop. They clone your repo, set up the development environment, write and test code, push changes for review, and keep working whether or not you’re online. They scale to thousands of workers via Kubernetes. And critically: your codebase, secrets, and build artifacts never leave your network.
The customers telling this story aren’t startups. Brex, a fintech company, says self-hosted agents will allow them to “delegate end-to-end software builds entirely to Cursor’s cloud agents.” Money Forward, a Japanese financial services provider with strict security requirements, is building a workflow for nearly 1,000 engineers to create pull requests directly from Slack. Notion calls it “a meaningful step toward making coding agents enterprise ready.”
This matters because it confirms what we’ve been seeing across the entire DevOps landscape: the agentic era demands self-hosted infrastructure, not cloud-only mandates.
The Self-Hosted Signal Is Everywhere
Cursor isn’t alone. Look at what’s happened in the last 90 days:
GitLab shipped Duo Self-Hosted GA, allowing enterprises to run selected LLMs on their own infrastructure for code suggestions and chat, explicitly addressing data sovereignty requirements.
Plane, the open-source project management platform, launched self-hosted AI with BYOK (bring-your-own-key) architecture in March 2026, giving enterprises AI capabilities inside their own security perimeter.
JFrog’s Secure Model Registry supports governance and deployment of AI/ML models across cloud and on-premises environments with a single click.
Even GitHub, the most cloud-native of the major platforms, is being pulled toward governed agent infrastructure. Their new Enterprise AI Controls and agent control plane shipped specifically because enterprises demanded visibility and policy enforcement for agent behavior.
The pattern is clear: every vendor that serves regulated enterprises is building self-hosted or hybrid-deployed AI capabilities. The market is rejecting the “cloud or nothing” premise.
What Cursor Shipped. And What They Didn’t
Let’s be specific about the architecture. Cursor’s self-hosted model uses a split design: a “worker” process runs inside the customer’s network, connecting outbound via HTTPS to Cursor’s cloud. Cursor’s agent harness handles inference and planning, then sends tool calls to the worker for execution on the customer’s machine. Results flow back for the next round of inference.
This is an elegant architecture for separating the AI reasoning (which runs on Cursor’s infrastructure) from the code execution (which stays in the customer’s environment). No inbound ports, no firewall changes, no VPN tunnels. For organizations scaling to thousands of workers, they provide a Helm chart and Kubernetes operator.
What Cursor shipped alongside this: isolated remote environments, multi-model support, plugin extensibility via MCP and subagents, and team permissions.
What Cursor did not ship: cross-toolchain governance.
Here’s what I mean. When a Cursor agent runs inside your network and pushes a PR at 2 AM, who audited what it did? When it connects to your Jira instance via MCP to update a ticket, who enforced which projects it can access? When you’re running 500 agent sessions across three teams, who tracks the total cost of model inference plus compute? When your compliance officer asks for evidence of what AI changed in your codebase last quarter, where does that evidence live?
These aren’t hypothetical concerns. NIST launched its AI Agent Standards Initiative in February 2026. The EU AI Act is in force, with its obligations phasing in. Gartner projects AI governance spending will hit $492 million this year. Every one of these frameworks demands documented governance for autonomous AI systems, not just team permissions and SOC 2 compliance.
Cursor built a great agent. They built reasonable security controls. They did not build a governance layer. Nobody has yet built one that spans toolchains.
The Three-Layer Enterprise Requirement
After working with enterprise customers in regulated industries over two decades, we see the self-hosted AI agent requirement breaking into three distinct layers:
Layer 1: Governed Infrastructure
The agents need a place to run. That place needs to be provisioned, secured, monitored, and compliant. For self-hosted deployments, this means Kubernetes clusters with proper RBAC, network policies, secrets management, and infrastructure-as-code. For air-gapped environments, the requirements are even more stringent.
Most enterprises don’t have the platform engineering capacity to stand up and maintain AI agent infrastructure at scale. They need a managed infrastructure layer that handles provisioning, scaling, patching, and monitoring, whether the deployment is cloud, self-hosted, or air-gapped.
This is what Reign Ops provides. Reign Ops operates the platforms your agents run on, 24x7, on infrastructure you control.
Layer 2: Runtime Security
Each agent session needs isolation guarantees. Cursor addresses this with dedicated VMs per session, which is a good start. But in multi-tool environments, where Cursor agents coexist with GitHub Copilot, GitLab Duo, and custom internal agents, runtime isolation becomes more complex.
The challenge we identified when we migrated our own agent infrastructure earlier this year was that runtime security requires process-level isolation, scoped credentials per agent session, rate limiting on tool calls, and deterministic boundaries on what each agent can access. Our approach uses containerized MCP server gateways where every external interaction is scoped, logged, and rate-limited. No agent gets broad credentials, and every tool call passes through an auditable gateway.
Layer 3: AI Governance Control Plane
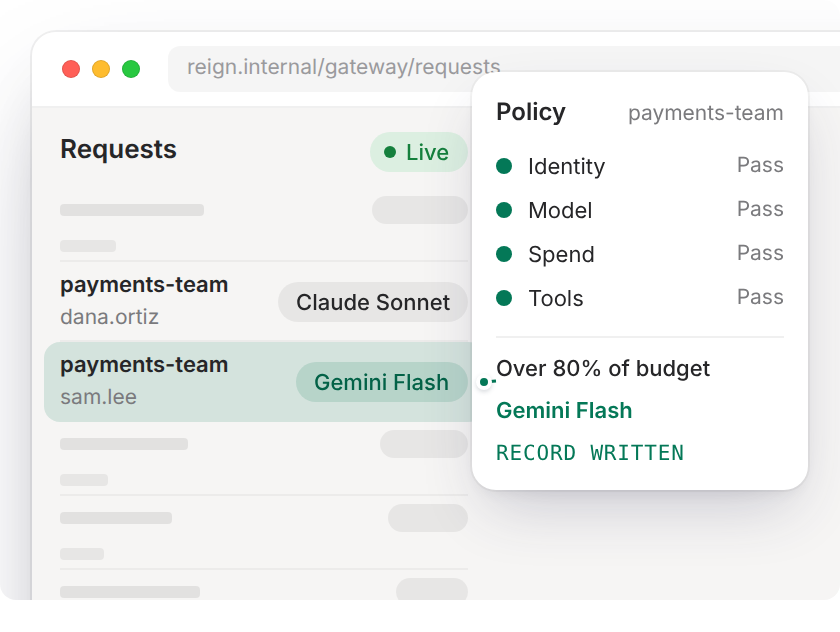
This is the cross-toolchain layer that no single vendor provides. When you’re running Cursor agents on self-hosted infrastructure alongside GitHub Copilot in the IDE and Rovo in your project management workflow, you need a unified governance layer that:
- Checks the identity of every person and agent that calls a model or tool
- Enforces policies consistently (which models, which tools, which limits)
- Tracks AI spend by team, project and agent
- Keeps a record of each call, in storage the institution owns
This is what Reign Gateway provides for the AI traffic sent through it: identity, policy, spend limits and a record of each model call. Agents never hold the provider keys.
The Convergence
Cursor’s self-hosted agents, Plane’s self-hosted project management, GitLab’s self-hosted Duo, JFrog’s hybrid model registry: these aren’t isolated product decisions. They’re a market-wide recognition that regulated enterprises need AI capabilities inside their security perimeter.
The vendors building the agents are getting better fast. What’s lagging behind is the governance infrastructure that makes those agents enterprise-ready at scale.
Reign Ops operates the platforms the agents run on. Reign Gateway governs the AI traffic sent through it. Together, they narrow the gap between “we have self-hosted AI agents” and “we can show our board, our auditors, and our regulators a record of what those agents did.”
The agentic era isn’t coming. It’s here. Cursor’s announcement is the latest proof point. The question isn’t whether your enterprise will run autonomous AI agents. It’s whether you’ll govern them before or after the first incident.
We’d rather help you do it before.
Paul Goldman
Founder and CEO, iTmethods
Founder and CEO of iTmethods. Writes Securing the Agentic Era, essays on governing agentic AI in regulated industries. His team runs the platform, does the work, and proves it.