DORA and AI Governance
Reviewed October 2026
DORA, the EU's Digital Operational Resilience Act, has applied since January 17, 2025. It requires financial institutions and their critical ICT service providers to demonstrate ICT risk management, incident reporting, resilience testing, and third-party risk management.
AI workloads operated by financial institutions fall under DORA's resilience requirements. That means AI governance in EU-regulated financial services is not only an EU AI Act obligation. It is also a DORA obligation, supervised by the same authorities.
What DORA Requires
DORA covers five operational domains and applies to financial institutions and critical ICT service providers:
- ICT risk management: documented, continuously maintained programs
- ICT-related incident reporting: tiered notification on strict timelines
- Digital operational resilience testing: regular, evidence-backed exercises
- ICT third-party risk management, including cloud and AI vendors
- Information-sharing arrangements across institutions and authorities
Major Incident Reporting Timelines
DORA sets tiered timelines for reporting a major incident:
- Initial notification: within four hours of classification (or 24 hours after detection, whichever is earlier)
- Intermediate report: within 72 hours of the initial notification
- Final report: within one month of the latest intermediate report
Where AI Workloads Intersect DORA
AI workloads are ICT systems. They generate ICT incidents. They depend on ICT third parties. They require resilience testing. An AI governance architecture that produces runtime evidence can supply the evidence your DORA program uses for AI workloads: the same audit trails and the same runtime controls.
Treating DORA and EU AI Act compliance as separate programs is expensive. The institutions that recognize the shared evidence-architecture pattern build once and produce evidence across both.
AI Vendors and the Register of Information
DORA requires each financial entity to keep a register of information on all its contractual arrangements with ICT third-party service providers. A model provider, an AI platform or a SaaS tool with AI features delivers an ICT service, so it belongs in that register, with the functions it supports and how critical they are. A change a vendor makes to how it uses your data is a change to an arrangement the register already records. For example, a model provider that supports a customer-facing workflow is recorded with that function, how critical it is, and the contract that governs it.
Sources
Unified evidence across DORA and the EU AI Act
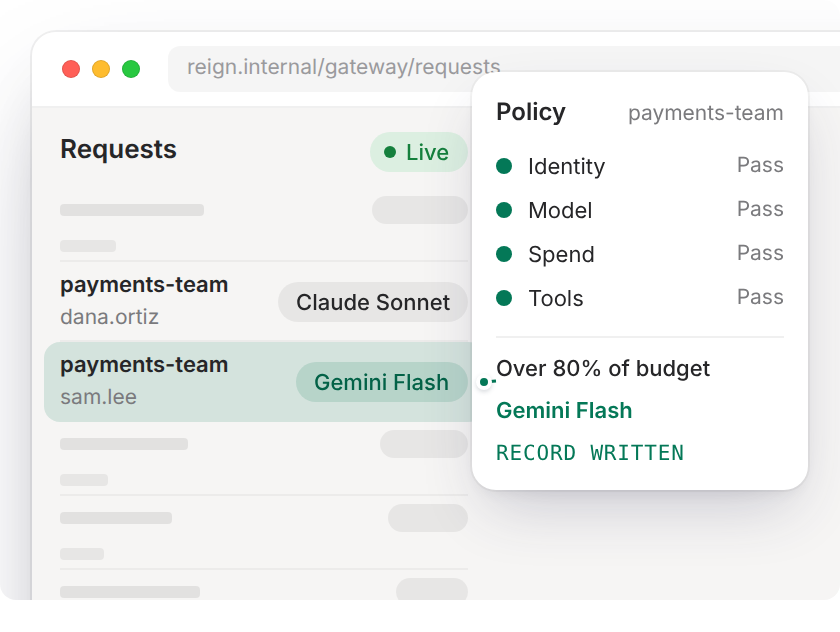
Reign Gateway records the request, the policy decision and the outcome for AI traffic sent through it: evidence your DORA program can use.