Most AI Governance Tools Were Built for Generative AI. Agentic AI Requires a Different Architecture.
Agentic AI is in production in regulated industries. The governance stack most institutions spent the last three years building was designed for a world that no longer exists. FINOS Open RegTech shows the architecture pattern that actually works.
Agentic AI is no longer theoretical in regulated industries.
Banks and insurers are deploying autonomous agents for trade execution, credit decisioning, fraud investigation, customer onboarding, and regulatory reporting workflows. Healthcare and life sciences are deploying agents for clinical trial coordination, lab data orchestration, and regulatory submissions. Public sector and critical infrastructure are not far behind. These systems do not just generate outputs. They take actions, call tools, maintain state across multiple steps, and interact with other agents.
That shift breaks the governance stack most institutions spent the last three years building.
Generative AI governance (the prompt-response, single-model, content-moderation paradigm) had a tractable problem: inspect the input, monitor the output, log what happened. The control surface was narrow. The decision was a piece of text. The auditability was after the fact.
Agentic AI removes every one of those simplifications. The control surface is every tool the agent can call, every system it can touch, every other agent it can coordinate with, and every piece of state it carries across a session. The decision is an action. The auditability has to be real-time, because by the time the action is logged, it has already executed.
Most existing AI governance tools, and most existing AI governance frameworks, were built for the prompt-response world. They are now being asked to govern a fundamentally different system. They will not.
The New Threat Surface
In late 2025, FINOS (the Linux Foundation’s Fintech Open Source Foundation) released Version 2.0 of its AI Governance Framework with a dedicated agentic AI risk catalog. It defines six new risks specific to autonomous architectures: multi-agent trust boundary violations, agent action authorization bypass, tool chain manipulation, MCP server supply chain compromise, agent state persistence poisoning, and agent-mediated credential harvesting.
These are not theoretical. MCP server supply chain compromise, where a tainted Model Context Protocol server feeds corrupted data or execution environments to agentic AI systems, is already surfacing in enterprise environments. Agent-mediated credential harvesting is, I expect, not far behind. The other four are arriving as fast as enterprise agent deployment is.
What is striking about the FINOS work is not the risk taxonomy itself (most serious AI security teams have parts of this list) but that it has been formally codified by a body whose institutional contributors include the largest banks in the world, and that it now maps to global regulatory frameworks including the EU AI Act, DORA, NIST AI RMF, ISO 42001, OWASP, and MITRE ATLAS.
Codified risks become procurement requirements. Procurement requirements become operating standards.
That progression is happening now.
This Is Not a New Problem. The Template Already Exists.
Here is what most people commenting on agentic governance are missing.
This is not the first time a regulated industry has had to build an evidence architecture for a novel control surface. Trade reporting solved a structurally identical problem over the last decade. Banks had millions of reportable events per day, generated by complex systems, governed by national variants of global regulations, with regulators demanding machine-readable proof that controls had run.
The solution was not a dashboard. It was an architecture.
The Common Domain Model (CDM), now hosted as a FINOS project, gave the industry a shared, machine-readable representation of trades and lifecycle events. Morphir, contributed by Morgan Stanley, gave the industry a way to express regulatory rules as executable code rather than as PDF interpretations. Digital Regulatory Reporting (DRR) wove the two together into a production layer that takes structured trade data, applies the rule logic, and produces reports a regulator will accept, automatically. Large banks, market infrastructure providers and central counterparties are now running this architecture in production.
The pattern is precise: take a regulatory requirement, express it as enforceable logic, run it continuously against operational data, and produce evidence as a byproduct of normal operations.
That pattern is exactly what agentic AI governance now needs. And the people who built the trade-reporting version of it, the same FINOS community, have just built the AI governance version with the AIGF. The bridge between the two is the strategic gap nobody has built.
Two Regulatory Domains. One Evidence Architecture.
A large regulated institution today has two governance problems that look completely different and are actually the same problem.
On one side: a trading or transaction operation generating millions of reportable events per day, governed by increasingly specific national implementations of global regulations.
On the other: an AI operation, with dozens or hundreds of models in production, agentic workflows in development and third-party AI embedded in SaaS across every business line, governed by an entirely separate and rapidly expanding regulatory framework.
Today these are separate compliance programs. Separate teams. Separate systems. Separate evidence collection processes. Separate audit responses.
But the underlying infrastructure problem is identical: take a requirement, express it as an enforceable control, run that control continuously against operational data, collect the evidence that it ran, and produce that evidence on demand.
CDM and DRR have proven this model works for trade reporting. The AIGF defines the equivalent for AI governance. What neither provides is the production layer that enforces the controls, collects the evidence, and makes it retrievable across both domains, on unified infrastructure.
Two regulatory domains. One evidence architecture.
The institution, or platform, that builds a unified evidence pipeline across both domains will define the architecture of regulatory technology for the next decade. Not because the regulations are the same, but because the infrastructure pattern is.
The Regulatory Clock Has Already Started
2026 is the year that trade reporting obligations and AI governance obligations hit the same institutions, under the same regulators, on overlapping timelines.
DORA has applied in full since January 17, 2025. Financial institutions and their critical ICT service providers must demonstrate ICT risk management, incident reporting, resilience testing, and third-party risk management. DORA’s tiered major incident reporting (initial notification within four hours of classification or 24 hours after detection, whichever is earlier; intermediate reports at 72 hours; final reports within one month).
EU AI Act high-risk enforcement was due on August 2, 2026 when this was published. (Editor’s note, October 2026: the Digital Omnibus on AI deferred stand-alone high-risk obligations to December 2, 2027 and high-risk AI embedded in regulated products to August 2, 2028. See The Deadline Moved. The Evidence Problem Didn’t.) Organizations deploying AI in credit scoring, recruitment, critical infrastructure, or biometric identification must demonstrate conformity assessments, risk management systems, and human oversight mechanisms. The evidence requirements are operational, not documentary. Regulators will ask for audit trails that prove controls ran, not policies that say they exist.
The EU Parliament has already flagged the overlap. Regulatory bodies are concerned about the interaction between the EU AI Act and EU financial services legislation, with a lack of sufficient guidance introducing complexity and legal uncertainty for institutions trying to comply with both simultaneously.
A large financial institution now faces DORA’s ICT resilience requirements, MiFID / EMIR / SFTR trade reporting obligations, and EU AI Act governance mandates, all enforced by overlapping regulatory authorities, all requiring continuous evidence, all running on infrastructure that must itself be governed.
Treating these as three separate compliance programs is the expensive way. The institutions that recognize the shared infrastructure pattern will build once and produce evidence across all three.
What the Right Architecture Actually Looks Like
It is worth being precise about what the right architecture is, because it is meaningfully different from what most institutions have today.
It is not a dashboard. Dashboards visualize what already happened. Agentic AI requires intervention before the action.
It is not a risk assessment tool. Risk assessments produce documents. Regulators are increasingly asking for runtime evidence.
It is not a policy management platform. Policies are inputs. Evidence is the output.
It is an engine that sits in the operational path of AI workloads: between the agent and the tools it can call, between the agent and the data it can read, between the agent and the systems it can act on. It evaluates every action against policy in real time. It allows, denies, or quarantines. And it produces, as a byproduct of every operation, the evidence that DORA, the EU AI Act, the AIGF and the trade-reporting frameworks ask for.
The parallel to DRR is exact. DRR takes CDM-structured trade data and produces regulatory reports. An AIGF-aligned evidence layer takes AI operational data (model invocations, agent actions, policy decisions, tool calls) and produces governance reports. Same pattern. Same infrastructure needs. Different regulatory domain.
Why Most Current Tools Will Fail
The gap is real because nobody is positioned to close it today.
Traditional GRC platforms, ServiceNow GRC and its peers, were built for policy management and checkbox compliance. They have no FINOS alignment, no AI-native architecture, and no ability to enforce policy at agent runtime. The evidence requirements coming from DORA and the EU AI Act are operational and continuous. GRC was built for a different problem.
The independent AI governance startups that existed in late 2024 have largely been absorbed into network and application security portfolios. Cisco acquired Robust Intelligence, and others have been folded into similar security stacks. None has FINOS alignment. None maps to the AIGF. None plays in the RegTech space. The acquisition pattern itself is the tell: the market recognized AI governance is infrastructure, but the acquirers embedded it in security stacks rather than regulatory architectures.
Model monitoring tools track performance and drift. They do not enforce policy at the moment of tool invocation, and they do not generate evidence a regulator will accept as a byproduct of operation.
The Big 4 consultancies implement compliance as large bespoke projects. They build bespoke; they do not operate managed platforms; they do not produce automated evidence at runtime. In RegTech, the project-based model is the model being disrupted.
REGnosys built Rosetta DSL, the language behind DRR. They are essential to the trade-reporting layer but have no AI governance capability and no managed infrastructure. Morphir is open source with no commercial offering. Together they prove the FINOS pattern; they do not operate it.
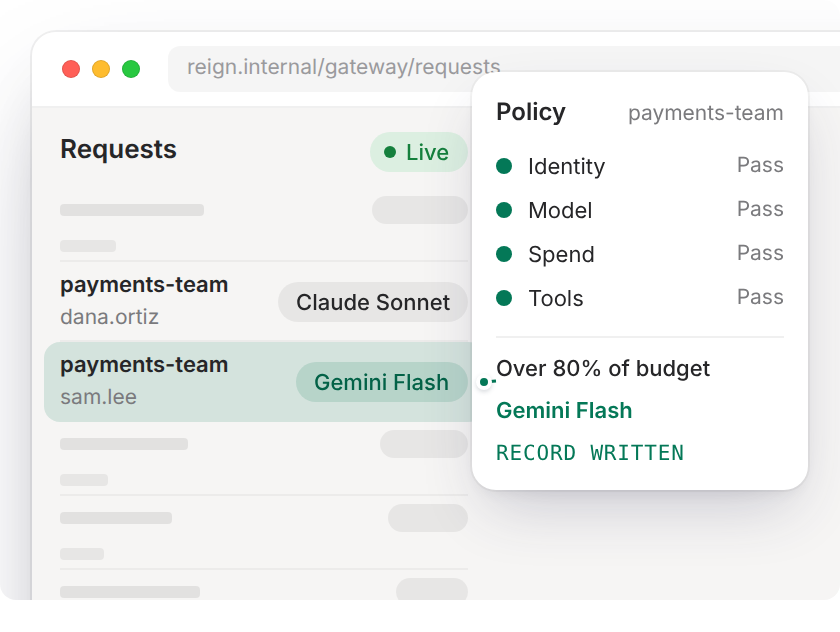
What Reign does today is narrower and concrete. Reign Gateway applies identity, policy and spend limits to the AI traffic sent through it and records each call in storage you own; Reign Ops operates the platforms beneath.
The Canadian Signal
There is an institutional dimension worth attention.
As of April 2026, three of Canada’s six Domestic Systemically Important Banks were FINOS members, and two of them sat on the FINOS Governing Board.
Canada’s banking regulator, OSFI, has been increasingly explicit about expectations for AI governance, model risk management, and operational resilience: E-23 on model risk, B-13 on technology and cyber risk, and forthcoming guidance on AI in financial services. These are not distant frameworks. They are the operating reality Canadian banks are building infrastructure to satisfy.
When Canada’s large banks are investing in the open-source regulatory infrastructure that will underpin compliance with these guidelines, the signal, on our reading, is that this is where institutional money is going. And the opportunity for managed infrastructure, for the institutions that want the benefits without operating the stack themselves, is wide open.
What Happens in the Next Twelve Months
Three developments will shape the coming year.
The FINOS RegTech Council will formalize. The institutions funding it will have outsized influence on the architecture of the next regulatory technology stack.
The AIGF will move from framework to procurement requirement. Institutions that contributed to v2.0 will begin requiring vendors and internal teams to demonstrate compliance against it as a condition of deployment. The AIGF Training Workshops running now are the leading indicator: you do not build a training curriculum for a standard you intend to leave optional.
Managed Open RegTech infrastructure will become an explicit market category. The largest global banks will continue building their own. The mid-tier banks, regional banks, insurers, asset managers, trust companies, and foreign-bank branches operating under regulators like OSFI, the FCA, BaFin, and FINMA will need someone to operate it for them, under SLA, with governance and continuous evidence production.
If you run technology, risk, or compliance at a financial institution, an insurer, or a life sciences organization trying to get ahead of the DORA / EU AI Act / MiFID collision, or if you are inside FINOS thinking about how the pieces fit together, I would like to have that conversation.
The Question
Most institutions today are still building governance for the world of 2024: the prompt-response world, where the control surface was narrow and the audit was after the fact.
The agentic era is already in production. The regulatory timelines have converged. The evidence architecture that will satisfy what is coming is the same across trade reporting and AI governance, because the infrastructure pattern is the same.
The components are proven. The institutional money is moving. The pieces are on the board.
The question is who assembles them first.
Paul Goldman
Founder and CEO, iTmethods
Founder and CEO of iTmethods. Writes Securing the Agentic Era, essays on governing agentic AI in regulated industries. His team runs the platform, does the work, and proves it.